Audit trails and change control in a regulated Intelex environment
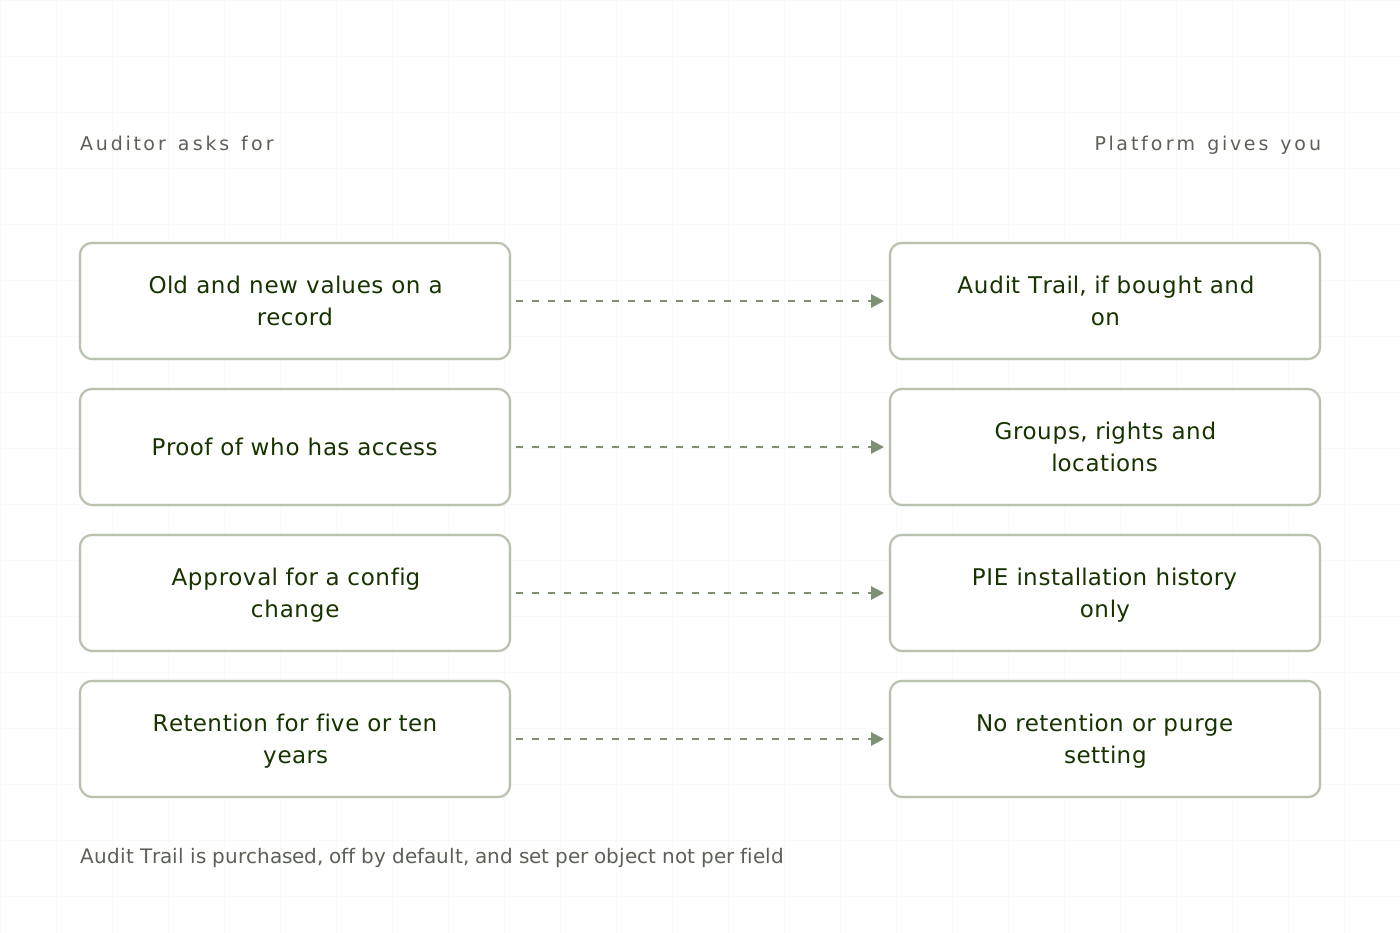
"This corrective action was closed on 14 March. Who changed the due date, and when?" Whether you can answer an auditor asking that in a regulated environment was decided months earlier, by a purchasing decision and a checkbox, and neither was framed as a compliance decision when it was made.
The Intelex audit trail is a purchased feature and is not on by default. Its granularity is per object, not per field: you audit the whole object or nothing. If nobody bought it, or nobody enabled it on that object before the change happened, the change history does not exist and cannot be recovered later.
What does the Intelex audit trail record?
Once purchased and enabled on an object, each entry captures:
Free
Read every article, in full.
- Every article on the site, start to finish
- Sources cited and linked on all of them
- New pieces on Intelex configuration and EHS practice
Would rather not sign up? Email me and I will send it over.